Exploring Key Subjects and Topics in the Data Protection Field
Data Privacy Laws and Regulations: Understanding the legal framework and compliance requirements related to data protection in various jurisdictions, such as the General Data Protection Regulation (GDPR) in Europe, the California Consumer Privacy Act (CCPA) in the United States, and other regional data protection laws.
- Information Security: Learning about different aspects of information security, including encryption, access controls authentication, firewalls, secure coding practices, and security incident response.
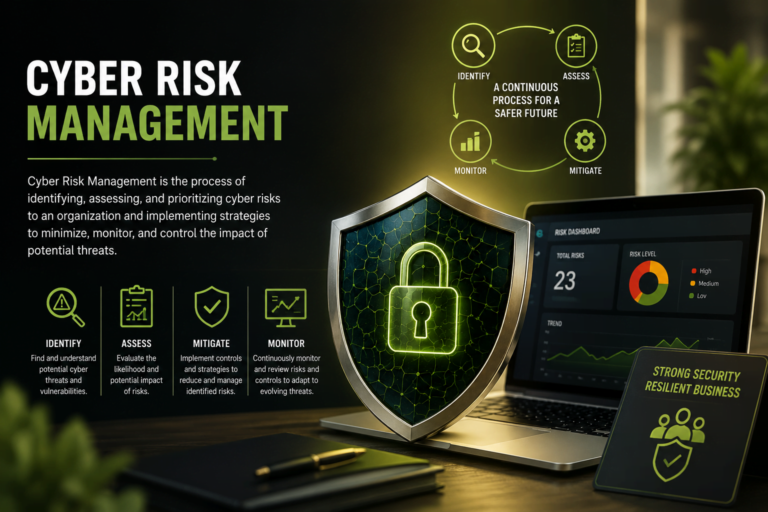
- Risk Management: Assessing and mitigating risks associated with data handling, storage, and transmission. This includes identifying vulnerabilities and implementing strategies to minimize the impact of potential data breaches.
- Data Governance: Establishing policies, procedures, and guidelines for the proper collection, storage, and usage of data within an organization.
- Data Ethics: Exploring the ethical considerations of data use and ensuring that data practices are aligned with ethical standards and respect individual rights.
- Data Privacy Impact Assessments (DPIA): Learning how to conduct DPIAs to assess the impact of data processing activities on individual privacy and identify measures to mitigate risks.
- Cybersecurity: Studying the protection of computer systems and networks from security breaches, hacking attempts, and unauthorized access.
- Information Technology (IT) Compliance: Understanding IT-related regulations and standards and ensuring data protection measures are in line with industry best practices.
- Data Breach Response and Incident Management: Preparing for and responding to data breaches or security incidents to minimize damage and comply with legal requirements.
- Privacy by Design: Integrating privacy measures into the design of systems, applications, and processes from the outset.
- Data Protection Technologies: Exploring tools and technologies that aid in data protection, such as data anonymization, tokenization, encryption software, and data loss prevention (DLP) solutions.
- Data Access Control: Implementing access control mechanisms to ensure that only authorized personnel can access sensitive data.
- Data Retention and Deletion: Establishing policies for data retention and secure deletion to minimize data exposure and comply with legal requirements.
- Cloud Computing Security: Understanding security measures and risks associated with storing and processing data in cloud environments.
- Third-Party Data Handling: Addressing data protection concerns when sharing data with third-party vendors or service providers.
- International Data Transfers: Complying with regulations regarding cross-border data transfers and the appropriate safeguards for such transfers.
- Data Protection Officer (DPO) Responsibilities: Understanding the role and responsibilities of a DPO, who is responsible for overseeing an organization’s data protection efforts.
Data protection is an ever-evolving field due to the constant emergence of new technologies, legal developments, and cyber threats. As such, professionals in this field need to stay updated and continuously expand their knowledge to effectively protect data and privacy.
some of the key subjects or topics of study involved include:
- Data protection law: This includes the study of the various laws and regulations that govern the collection, use, and sharing of personal data. Some of the most important laws in this area include the General Data Protection Regulation (GDPR), the California Consumer Privacy Act (CCPA), and the Brazilian General Data Protection Law (LGPD).
- Data protection principles: These are the fundamental principles that guide the collection, use, and sharing of personal data. Some of the most important data protection principles include the principles of lawfulness, fairness, transparency, purpose limitation, data minimization, accuracy, storage limitation, integrity and confidentiality, and accountability.
- Data protection techniques: These are the methods and tools used to protect personal data from unauthorized access, use, disclosure, modification, or Destruction. Some of the most important data protection techniques include encryption, pseudonymization, data masking, and access control.
- Data protection compliance: This is the process of ensuring that an organization’s data protection practices comply with the applicable laws and regulations. This process typically involves conducting data protection assessments, implementing data protection policies and procedures, and training employees on data protection best practices.